
The images in this article were generated with artificial intelligence. How we publish
The appearance and rapid circulation of ACR Stealer - also referred to in some reports as Amatera or AcridRain in its commercial evolution - again highlights a simple and painful lesson: many sophisticated intrusions begin with a banal human gesture. A user who sticks and runs a command in the Run box is, in practice, the master key that opens a corporate network And that doesn't fix patches or software updates.
The two delivery paths described by Microsoft show a range of modern techniques: a fully phileless chain that abuses mshta.exe, VBScript and a JPEG image that contains the payload in its pixels; and another that writes disk components from a WebDAV resource, starts a legitimate Python binary and persists with programmed tasks that simulate updates. The common denominator is social engineering and direct execution of orders by the user not the exploitation of a technical failure.
The consequences are clear and dangerous: ACR access passwords saved in browsers, live session tokens, PDFs and synchronized documents from OneDrive and SharePoint. That makes a committed machine an open door to corporate accounts and shared data. Microsoft and response teams recommend, in addition to isolating host, revoking access tokens and not just rotating passwords, because tokens can continue to authorize sessions even after changing keys.
The use of embedded payload images and legitimate file accommodation (ImgBB, image services, WebDAV) complicates detection, and techniques such as EtherHering - where addresses or signs are published in smart contracts in public blockchains - make part of the infrastructure difficult to neutralize. The attack is based on legitimate tools and services to hide and persist, so traditional signature-based telemetry fails against these variants.
From a defensive point of view, two realities have to be accepted: the first, classical technical prevention does not eliminate social vectors; the second, there are administrative and hardening controls that do greatly reduce the opportunity window of the attacker. Measures such as removing the Table Run by group policies, blocking mshta.exe with AppLocker or WDAC, applying application control and attack surface reduction rules so that PowerShell, Python or rundll32 cannot run downloaded content from% LocalAppData% or Temp are concrete and effective actions.
In detection, attention to behavior is key: processes such as rundl32.exe that establish network connections without clear parameters, reflective calls in memory, unusual activity towards image hosts or WebDAV mounts are commitment indicators that deserve immediate research. Proactive Hunting, Rapid Isolation and the revocation of credentials and tokens should be part of the response procedures to cut off side access and exfiltration of sensitive devices.
The public narrative about ACR also provides a warning about threat intelligence: reports often show representative parts of infrastructure and behaviour, but do not give complete numbers or firm powers. Microsoft has been cautious not to bind a specific actor and to describe the family for its behavior; those who operate and sell these tools change names and panels, so the labels evolve while the technique persists.
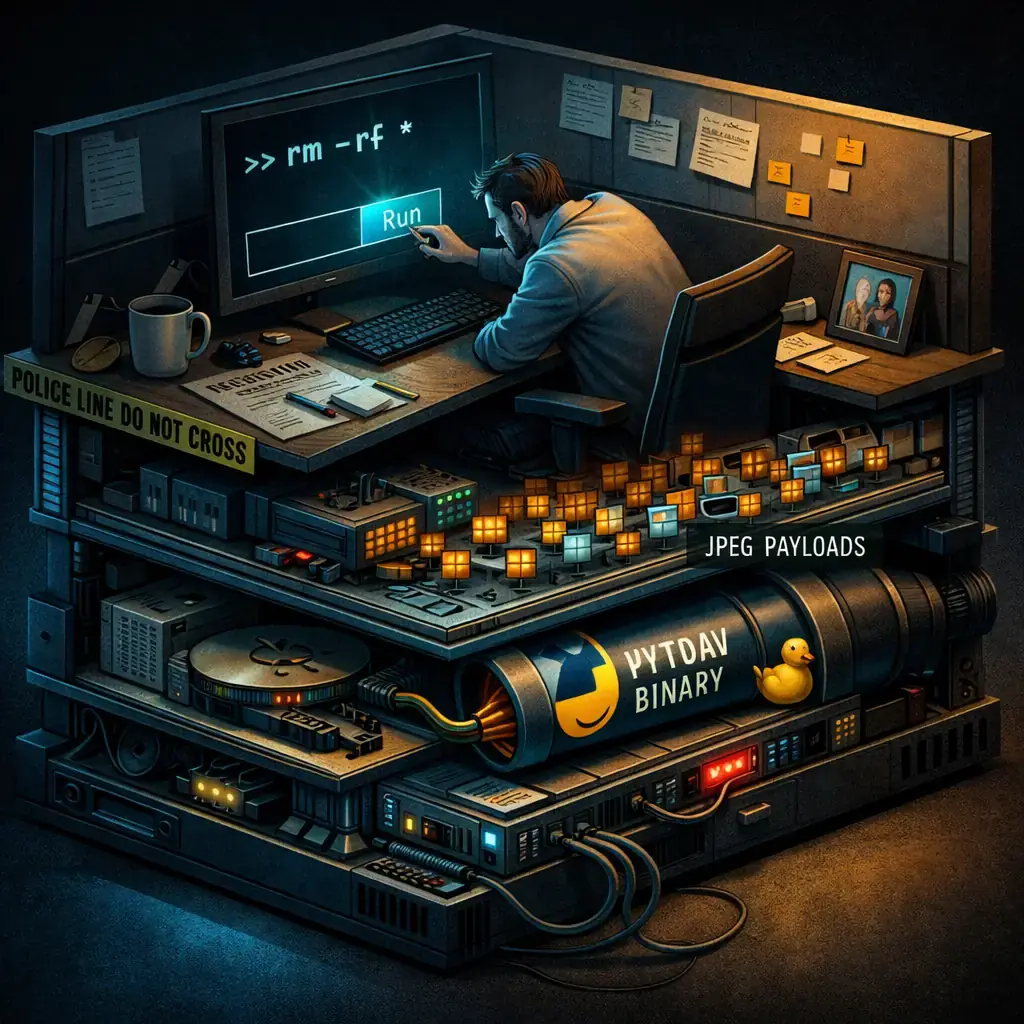
For business security officials: do not delegate all the defence to the patches or to the antivirus firm. Combine technical controls (AppLocker / WDAC, execution policies, mshta block, performance restrictions from Downloads / Temp), risk-focused training to paste and run commands and operating procedures to revoke tokens and audit OneDrive / SharePoint synchronies. Check programmed tasks with suspicious names and timestomping and PowerShell history erasing searches.
The community and response teams offer useful materials for implementing countermeasures and hunting searches; they should be consulted and adapted to their own environment. Microsoft publishes guides and detections on its security blog, and the SANS Internet Storm Center maintains bitácoras and analyses that help understand infection chains based on maldumping or malicious SEO. See, for example, Microsoft's security blog in https: / / www.microsoft.com / en-us / security / blog / and the SANS ISC's repository of articles and diaries https: / / ist.sans.edu / to deepen.
In short, ACR Stealer is a reminder that effective security blends technology, processes and people: closing this entry path requires restricting endpoint and policy capacities, improving session and tokens hygiene, and sustaining behavior-based surveillance that detects when legitimate tools are used for malicious purposes. If your organization has not yet reviewed controls on mshta, execution from temporary folders and tokens revocation procedures, this review should be up to the top of priorities.

FBI and six countries link Integrity Technology Group to entity post theft in SE Asia
On October 8, the FBI and agencies in six countries issued a joint warning that assigns to a Chinese company, Integrity Technology Group, a sustained series of intrusions whose ...

Campaign with LLM and ARTEX attacks South Korean financial institutions and exfilters data
Security researchers have documented a campaign directed against South Korean financial institutions using language-driven attack tools to automate intrusions and data extractio...

ChainDrop campaign exposes tensorlake in npm; version 0.5.144 withdrawal
A package of npm called tensorlake, an SDK in TypeScript oriented to Tensorlake applications and services, was engaged in a supply chain campaign linked to the attack family kno...

Cyber risk in 2026 moves to workflows and IA, according to Voice of the CISO
The data added by five editions of the Voice of the CISO study - including the most recent findings of 2026 - draw a less intense change than risk location: the threat is moving...

Phishing BitB points to advertising professionals and account managers to steal MFA
Security researchers have described a phishing campaign for advertising professionals and account managers that uses a human-operated platform to mimic ad products linked to IA ...

LibreOffice / OpenOffice Calc allows remote source execution when opening ODB / JDBC leaves
Researchers have shown that a malicious spreadsheet can force LibreOffice and Apache OpenOffice to run code controlled by an attacker at the time the file is opened, without sho...

Denmark confirms unauthorized access to the RCP that affected 8.8 million records
The Danish government confirmed that for about ten days in September there were unauthorized access to the Central Peru Register (CPR) the national population database. Accordin...