
The images in this article were generated with artificial intelligence. How we publish
A new cyberespionage operation baptized by researchers like Operation Dragon Weave has put into evidence increasingly sophisticated tactics to compromise public and private objectives, with reports focused on the Czech Republic and Taiwan. The attackers have combined targeted social engineering with multi-stage execution chains and legitimate cloud services to hide command and control communication, which complicates detection by traditional controls.
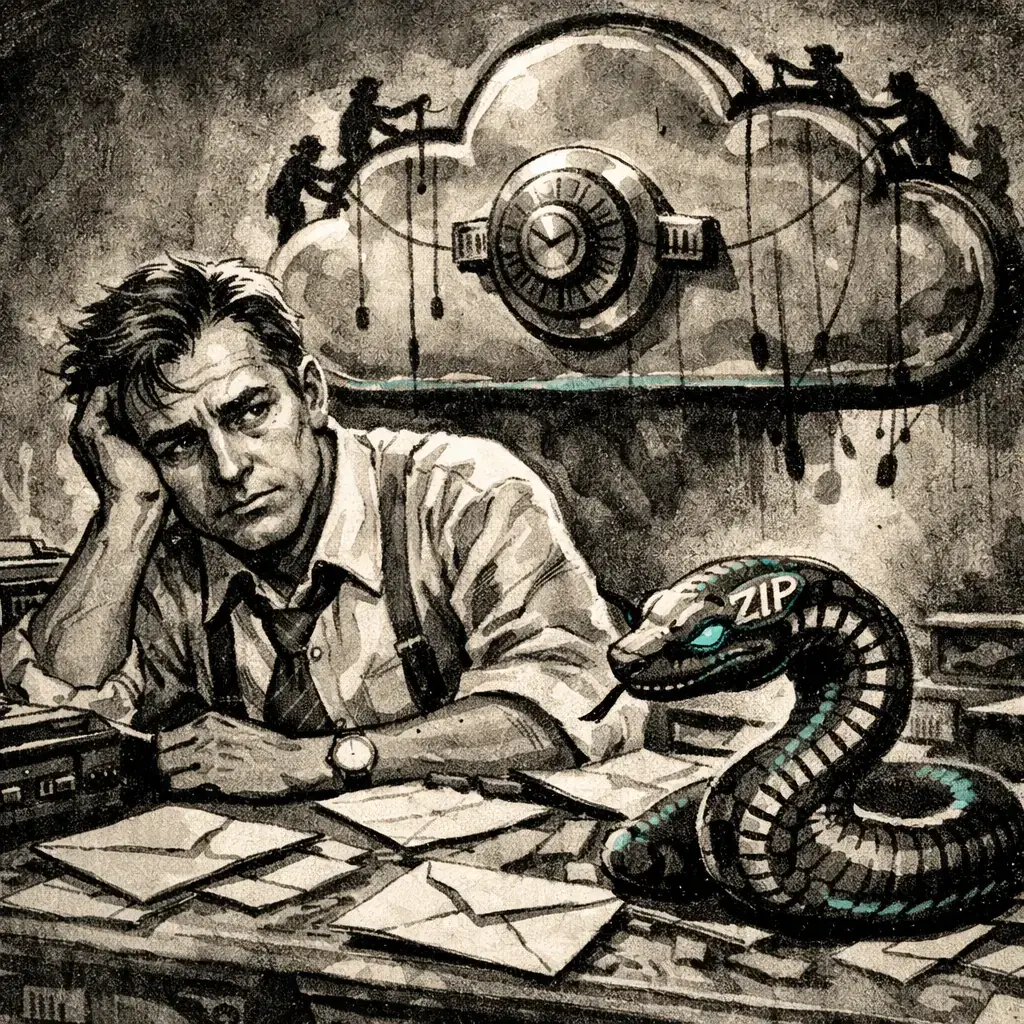
The initial vector described consists of speed-phishing emails containing ZIP files with several components that appear to be benign. Among these artifacts are direct access to Windows (.LNK) disguised as PDF documents that, when opened, release PowerShell scripts to reach an intermediate executable; in other cases the ZIP contains a self-sufficient binary written in Rust that acts as a dropper. Both routes converge in the execution of a binary called "RuntimeBroker _ update.exe," which it uses DLL side-rolling to load a malicious DLL and deploy a loader in Rust (called RUSTCLOAK) that finally disfigures and runs a remote control agent known as AZUREVEIL.
The element that makes AZUREVEIL particularly concerned is its communication model: instead of directly contacting command and control servers, it operates by means of a "dead drop" mechanism in Microsoft Azure Blob Storage where the attacker and the engaged machine exchange information in a common storage container. The use of widely legitimate cloud services complicates the identification of malicious traffic, because it is mixed with millions of legitimate calls to the platform. Microsoft documents the operation and management of Blob Storage, which is the same piece of infrastructure that these actors are abusing: https: / / learn.microsoft.com / en-us / azure / storage / blobs / storage-blob-introduction.
In addition to AZUREVEIL, analysts have identified contemporary activity of other toolkits and backdoors linked to groups aligned with China, including developments in Go and reuse of open-source frameworks to create custom implants. Reports and analysis of security signatures such as Unit 42 and ESET show a sustained pattern of campaigns that mix living-off-the-land techniques, modularity in the delivery and use of hybrid infrastructure to maintain persistence and scalation of privileges: https: / / unit42.paloaltonetworks.com / and https: / / www.eset.com / int / research /.
The implications for organizations and users are clear: the combination of speed-phishing with artifacts that seem legitimate, useful loads in Rust / Go and the abuse of cloud services means that traditional perimeter controls are not enough. A successful intrusion can provide total remote access, data exfiltration, internal pivoted and the ability to run code in memory without leaving persistent binary obvious This increases the risk to both government entities and the critical private sector.
Specific and coordinated measures are required to identify and mitigate these threats. In endpoints it is essential to have EDR solutions that inspect the execution of unusual child processes (e.g., LNK invoking PowerShell), monitor the dynamic load of DLs and alert about typical loaders and memory opuscation behaviors. The application of execution lock policies for .LNK files, the disabling of unnecessary macros and the restriction of PowerShell to signed or advanced recording modes reduces the initial attack surface.
In the network and cloud layer, it is appropriate to implement the Azure Storage account and container logging, to enable diagnostics and alerts on abnormal access patterns, and to restrict permissions to containers through restricted access policies and the rotation of credentials / SAS. All organizations that use cloud storage services should audit who can read and write in each container, because the abuse of a legitimate remedy can serve as a covert channel of C2.
The preparation and response to incidents should include playbooks for attacks that use dead drops in the cloud. In the face of a suspicion of commitment, disconnect the affected equipment from the network, preserve memory and disk dumping for forensic analysis, and review the access log to cloud storage are critical steps. It is also recommended to coordinate with cloud suppliers to block suspicious containers and obtain access metadata that will enable the activity of the opponent to be traced.
From a governance and training perspective, prevention begins with human risk reduction: Spear-phishing awareness campaigns targeting personnel with access to sensitive information, simulated phishing exercises and regular privilege reviews help to reduce the likelihood of success of an initial attack. At the technical level, technologies like Application Control, blocking DLL side-rolling by managed lists, and network segmentation limit the attacker's ability to move laterally.
Finally, it is important for organizations to share indicators and tactics with the community and intelligence providers to improve collective detection. The threats evolve rapidly: the re-use of open-source frameworks and the adoption of modern languages such as Rust or Go by attackers require the updating of detection rules and forensic capabilities. Keeping yourself informed through sources of trust and adapting controls accordingly is more than ever an operational need.

FBI and six countries link Integrity Technology Group to entity post theft in SE Asia
On October 8, the FBI and agencies in six countries issued a joint warning that assigns to a Chinese company, Integrity Technology Group, a sustained series of intrusions whose ...

Campaign with LLM and ARTEX attacks South Korean financial institutions and exfilters data
Security researchers have documented a campaign directed against South Korean financial institutions using language-driven attack tools to automate intrusions and data extractio...

ChainDrop campaign exposes tensorlake in npm; version 0.5.144 withdrawal
A package of npm called tensorlake, an SDK in TypeScript oriented to Tensorlake applications and services, was engaged in a supply chain campaign linked to the attack family kno...

Google reports DNS kidnapping: TLS certificates for google.com.gh, google.sl and google.as
Google reported on October 6 that attackers managed to issue unauthorized HTTPS certificates for Google and YouTube names after compromising authoritative DNS records of three t...

Cyber risk in 2026 moves to workflows and IA, according to Voice of the CISO
The data added by five editions of the Voice of the CISO study - including the most recent findings of 2026 - draw a less intense change than risk location: the threat is moving...

Phishing BitB points to advertising professionals and account managers to steal MFA
Security researchers have described a phishing campaign for advertising professionals and account managers that uses a human-operated platform to mimic ad products linked to IA ...

LibreOffice / OpenOffice Calc allows remote source execution when opening ODB / JDBC leaves
Researchers have shown that a malicious spreadsheet can force LibreOffice and Apache OpenOffice to run code controlled by an attacker at the time the file is opened, without sho...