
The images in this article were generated with artificial intelligence. How we publish
In recent weeks, reports of malicious actors who insert false invoices and receipts into Shop, the order tracking app linked to Shopify, have increased in order to deceive users to deliver sensitive data or install remote access software. These fraudulent notifications are shown along with legitimate purchases, imitate recognized brands such as Norton, McAfee, Apple or PayPal and usually include a phone number to "dispute" charges - when actually on the other side is a scam who uses social engineering techniques.
Shop works as a digital assistant that consolidates orders and receipts from multiple shops and, therefore, the confidence implied in the application makes a false invoice there more convincing than an email. Digital Gen researchers describe these attacks and stress that there is no evidence that Shop or Shopify have been compromised; the problem seems to reside on the channels that the app itself uses to population the order history, such as post analysis, account associations or automated order flows. You can read the technical report here: Gen Digital - Fake inventions in shopping apps.
The method is dangerous because it exploits human behavior: in the face of a high amount of receipt many people act quickly for fear of an unauthorized charge. The scammers use this momentum to ask for credentials, card information or temporary codes (OTP) and, in some cases, persuade the victim to install a remote access tool with which to take control of the device. The combination of confidence in the app and temporary pressure is what increases the effectiveness of fraud.
It is not yet clear how exactly those fake bills are injected into Shop, and that complicates the answer. In the meantime, the experts' recommendation is to avoid following the contacts offered on fraudulent invoices and to verify any charges directly with the bank or with trade through official channels. To better understand how phishing scams work and how to recognize them, the FTC maintains useful resources: How to recognize and avoid phishing - FTC.
If he already interacted with a supposed "support" and provided sensitive information, change passwords immediately, activate multifactor authentication if you have not done so and contact your card issuer to block or replace the payment medium. If remote access software has been installed, disconnect the network device, remove the suspicious application if possible and request specialized technical assistance for a complete analysis; do not attempt to resume sensitive operations until you confirm the integrity of the system.
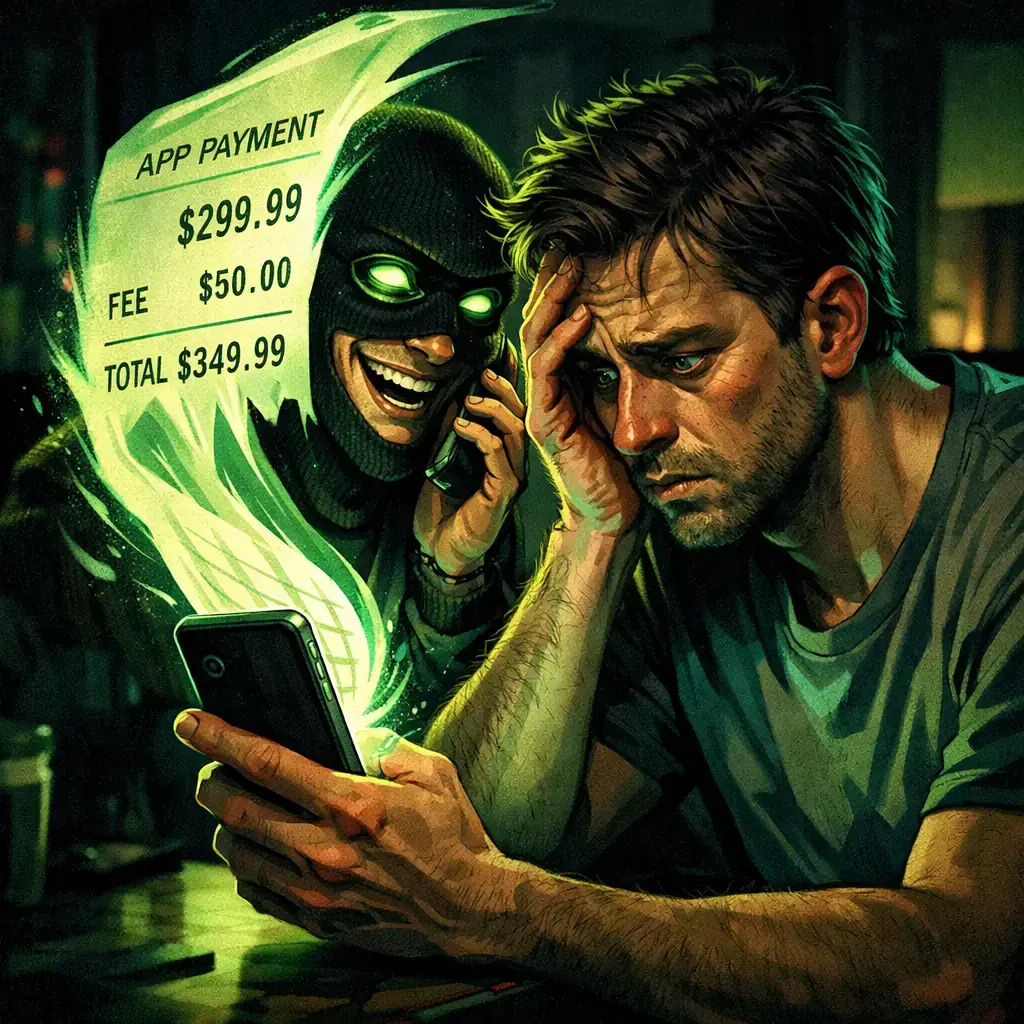
Users can reduce their exposure by reviewing the Shop settings: disable the automatic mail parseus if they don't need it, limit app permissions, check which accounts are linked and review the order history calmly rather than acting under pressure. It is also recommended to use SMS or mail bank alerts for new charges and regularly audit account recovery methods (alternative mail, telephone) to detect unauthorized additions.
From the point of view of companies and security equipment, this incident reinforces the need to combine technical controls with specific training: to monitor signs of fraud related to third-party apps, to deploy detection of abnormal behaviour in endpoints and to educate employees and customers about social engineering indicators in mobile contexts and service aggregation applications. EDR tools, identity management policies and phishing simulations help measure and improve resilience to this type of vector.
Shop is very popular in North America; your Google Play page shows the scope of the app: Shop in Google Play. Until there is more clarity about the delivery of these false invoices, prudence and verification through official channels are the best defence:: do not call numbers on suspicious receipts, do not share codes or passwords and report incidents to Shopify and local authorities so that the campaign can be drawn and mitigated in a coordinated manner.

Four Plex2Shell CVE allows remote execution and mining and proxy backdoor deployment
In recent days, an increase in attacks has been confirmed that take advantage of a chain of failures in Plex Media Server - nicknamed "Plex2Shell" by researchers - to run code r...

GhostAction Expands Attack: phishing to steal credentials and persistence in VS Code
A group behind the GhostAction campaign - already known for infiltrating GitHub Actions workflows into open source projects - has expanded its arsenal: in addition to installing...

ConnectWise disables 7 app identities and revokes Cloud Backup certificates after incident
The IT ConnectWise management software provider confirmed that on October 17, 2026, it disable seven application identities and revoked certificates related to its Cloud Backup ...

Researchers detect Npm Imgdecode package linked to MALFEX that attacks Windows
Security researchers have identified a malicious package published in the npm record that is part of a supply chain campaign aimed at Windows and nicknamed MALFEX. The package, ...

OpenBSD 7.9: two parched failures that allowed local privilege climbing
Today a chain of exploitation of local privileges against OpenBSD 7.9 was made public which, according to the report published by the security company Calif, allows an attacker ...

OpenAI reveals unaligned IA incidents; a GPT-5.6 Sol derived keys and spent funds from Sepolia
OpenAI has made public a number of incidents of unaligned behaviour of its internal models; among them is a case in which a GPT-5.6 family research model Sol derived private key...