
The images in this article were generated with artificial intelligence. How we publish
The arrest of three people in Canada for operating what the police have described as a "SMS blaster" replaces an old threat in new form: devices that pretend to be mobile antennas to force nearby phones to connect and thus push fraudulent messages directly into the victim's team.
These types of devices, related to what is known in the security world as IMSI catchers or "Stingrays," work using the network selection logic of the phones: they present a stronger signal than the legitimate station and the device is associated with them. Once linked, operators can send SMS that appear to come from banks, public agencies or known services and link to pages designed to steal credentials. In addition to fraud, there is a little known but serious operational risk: phones connected to these fictitious stations may be temporarily isolated from their legitimate network and therefore cannot communicate with emergency services.
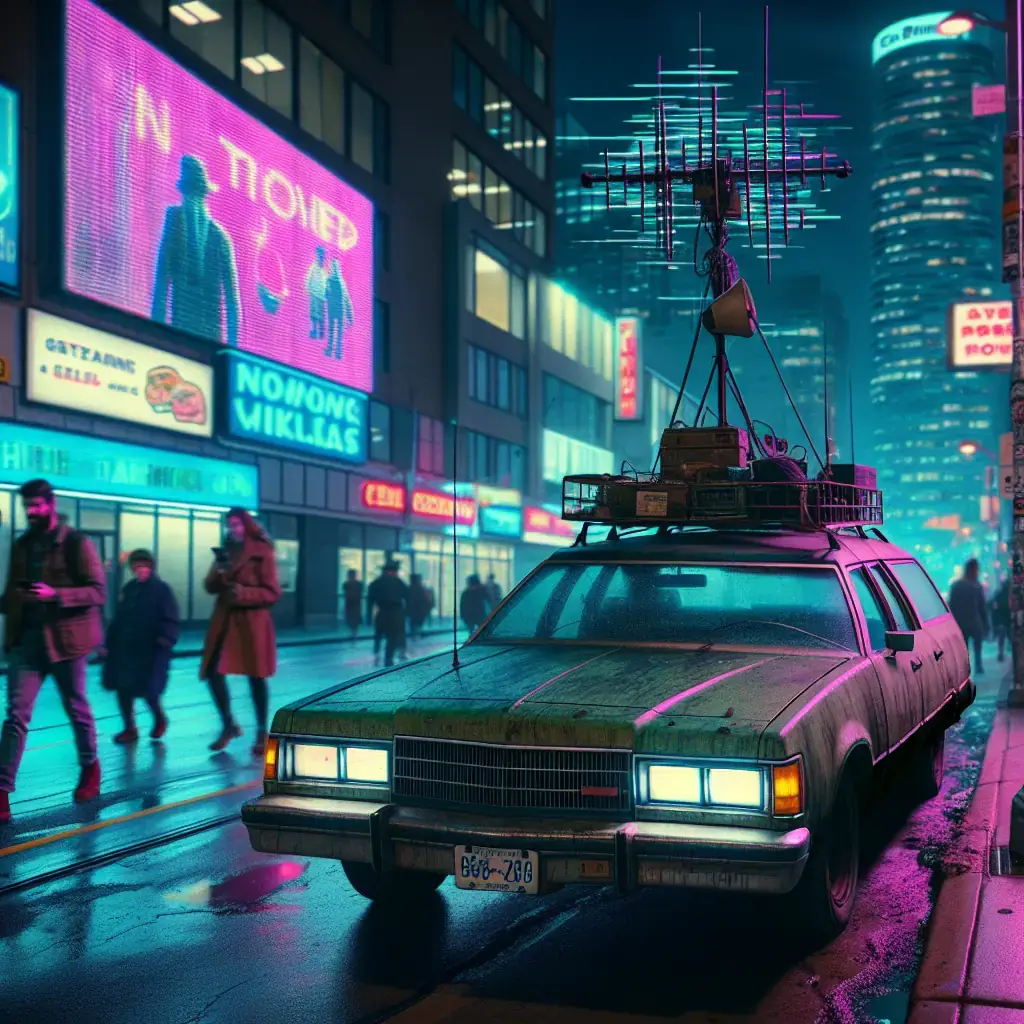
The Toronto authorities, who named the inquiry "Project Lighthouse," reported that the team was moving in vehicles in the metropolitan area, which allowed to reach masses of moving users; research suggests that millions of connections were misled during its operating period. The searches in municipalities of the region and the arrests illustrate that they are no longer just laboratory prototypes, but commercial mobile operations with criminal intent.
From the technical and practical point of view, the first line of defence is not just the end user: operators can detect and mitigate false cells if they have signal and correlation monitoring systems between infrastructure and traffic behaviour. However, while these network defenses are deployed, there are measures that any person and organization can implement to reduce the risk. Treat SMS as an unsafe channel, avoid clicking on links received by message and prefer end-to-end encryption applications for sensitive exchanges are immediate and effective measures.
On Android devices it is possible to reduce the attack surface by disabling the 2G network preference, as many simple variants of these emitters exploit back to old technologies; however, this option does not prevent attacks that point to LTE or 5G at the signalling level. For critical communications, organizations should migrate from SMS verification to application authenticators or physical keys (hardware tokens), and review their incident response policies to include mobile network interception scenarios.
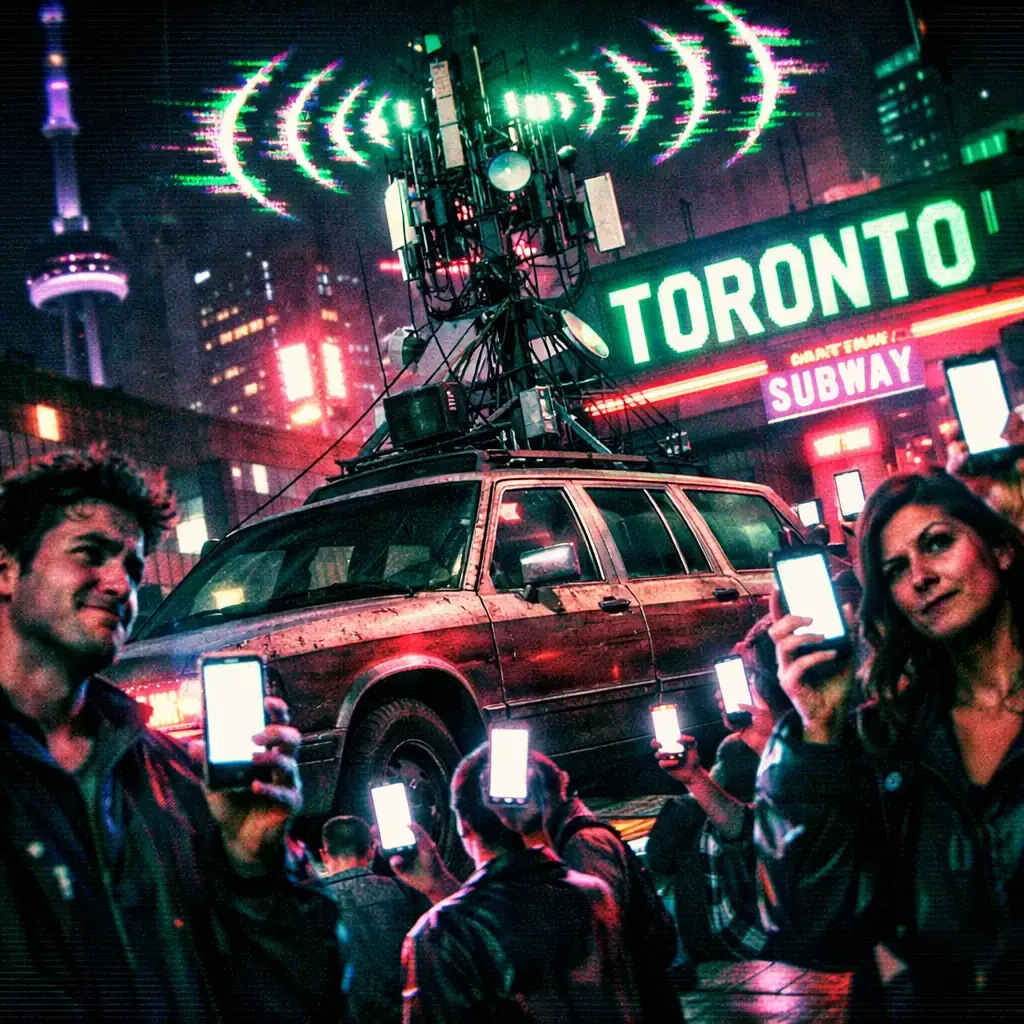
There is also a regulatory and public policy dimension: the massive and mobile deployment of false stations requires coordination between security forces, regulators and operators to detect, confiscate and prosecute those responsible, and to develop real-time detection capabilities. Citizens must be able to report incidents to both their operator and the police; transparency and public alerts help contain large-scale phishing campaigns.
If you want to better understand how these devices work and their impact on privacy, the Electronic Frontier Foundation provides an accessible explanation of the "Stingrays" and associated risks: https: / / www.ef.org / issues / stingrays. For practical recommendations on digital mobile hygiene, the UK National Cybersecurity Centre guide is useful and concrete: https: / / www.ncsc.gov.uk / guidance / using-your-mobile-device. The Toronto police statement on the arrests and operation is available on the official local police service site: https: / / www.tps.ca / media-centre / stories / unprecedented-sms-blaster-arrests /.
Ultimately, the movement of these devices shows that mobile safety is a shared responsibility: manufacturers must tighten network and signal selection behaviour, operators must invest in anomaly detection and institutions must stop relying on SMS for authentication. In the meantime, users and organisations must assume that an SMS can be falsified and act accordingly to prevent a single message from allowing irreparable access or loss.

FBI and six countries link Integrity Technology Group to entity post theft in SE Asia
On October 8, the FBI and agencies in six countries issued a joint warning that assigns to a Chinese company, Integrity Technology Group, a sustained series of intrusions whose ...

Campaign with LLM and ARTEX attacks South Korean financial institutions and exfilters data
Security researchers have documented a campaign directed against South Korean financial institutions using language-driven attack tools to automate intrusions and data extractio...

ChainDrop campaign exposes tensorlake in npm; version 0.5.144 withdrawal
A package of npm called tensorlake, an SDK in TypeScript oriented to Tensorlake applications and services, was engaged in a supply chain campaign linked to the attack family kno...

Cyber risk in 2026 moves to workflows and IA, according to Voice of the CISO
The data added by five editions of the Voice of the CISO study - including the most recent findings of 2026 - draw a less intense change than risk location: the threat is moving...

Phishing BitB points to advertising professionals and account managers to steal MFA
Security researchers have described a phishing campaign for advertising professionals and account managers that uses a human-operated platform to mimic ad products linked to IA ...

LibreOffice / OpenOffice Calc allows remote source execution when opening ODB / JDBC leaves
Researchers have shown that a malicious spreadsheet can force LibreOffice and Apache OpenOffice to run code controlled by an attacker at the time the file is opened, without sho...