
The images in this article were generated with artificial intelligence. How we publish
When Gartner decides to coil a new technological category, it is not a minor gesture: it is often the conclusion that one way of doing things no longer works in the face of the real challenges that organizations face today. That is the sense of the emergence of the Exposure Assessment Platforms (EAP), a family of solutions that tries to replace the old vulnerability management paradigm focused on static CVE lists with a dynamic vision that models how an attacker can move within a complex environment. You can see an introduction to this concept in a market supplier's own EAP definition Here., and the formal evaluation of the category appears in Gartner's recent Magic Quadrant about Exposure Assessment Platforms.
The problem was not only that traditional tools generated noise; it was that most of that noise did not reduce real risk to business. Security teams have spent years chasing endless lists of vulnerabilities - many of them in assets that in practice do not offer a viable path to critical systems - and the result has been a double defeat: warning fatigue and little impact on the organization's effective exposure. In internal studies and field analysis it has been found that a high proportion of findings correspond to what some call "dead ends," active without a feasible path for an attacker to reach valuable resources; that observation is precisely the engine of the PEF proposal.
The key idea of these platforms is to stop assessing vulnerabilities in isolation and start assessing exposure as a moving phenomenon. Instead of offering a list ordered by CVSS score, EAP assemble inventory, configuration, identity and control signals to map real attack routes: how an account with excessive privileges, an unmonitored machine and an exposed door can be combined to allow a serious engagement. This modeling form collects the logic of frames like MITRE ATT & CK, which shows how adversaries chain techniques to advance within a target.
The transition to this approach has practical implications. First, prioritization is no longer based solely on technical severity and is going to consider the context: whether a vulnerability is on an isolated server or a service with routes to high-critical assets makes a huge difference. Second, integration with operational flows becomes essential: it is not worth labelling a risk if it is not possible to assign, track and verify mitigation in marketing tools, CMDB or ITSM. And third, the measurement of success changes: the goal is no longer "how many vulnerabilities we park," but "how many critical ways of attack we have eliminated or mitigated." Gartner reflects this change of approach in its market assessment and projects significant impacts for availability and operational resilience if organizations adopt this approach.
It is also important to understand the maturity of the market. In observing the suppliers, two groups are distinguished: companies that try to add exposure capabilities on traditional scanning engines and native players that have thought since the design on modelling of attack routes and continuous testing. This difference is reflected in the implementation experience and the quality of the models generated by the platforms. The more mature solutions deliver actionable exposure maps that allow to focus efforts on what really reduces business risk.
From the perspective of the security team, change brings tangible advantages. Redirect resources to interventions that cut off attack paths reduces lost time and improves the traceability of the mediation effort. In addition, incorporating metrics that reflect real exposure to business makes it easier to communicate priorities to management and justify investments. Organizations such as CISA and reference standards such as the NIST guidelines on vulnerability management Remember that risk and context-based management is more effective than pure reactive mediation.
We must not lose sight, however, of the fact that the adoption of EAPs requires organizational and technological changes. Equipment must accept new metrics, create processes that connect findings with IT operations and define clear rules on ownership and resolution times. It is also necessary to review integration with clouds, identity directories and detection tools so that the exposure model reflects operational reality. In practice, this usually involves pilots who validate the value, check whether the platform highlights real attack routes and measure risk reduction after specific interventions.
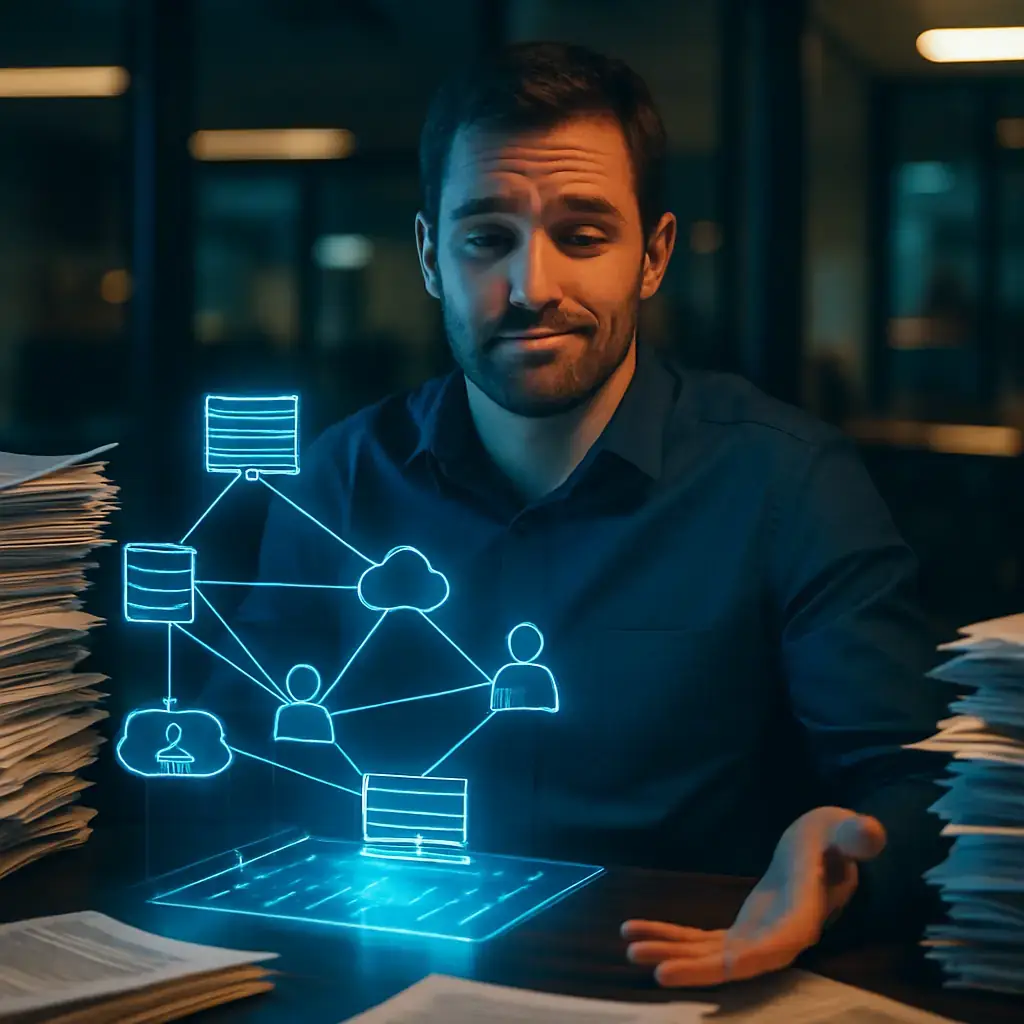
If your organization is rethinking its vulnerability strategy, it is appropriate to evaluate with a practical approach: does the tool model real and verifiable attack routes? Does it connect identity, cloud and on-premises on a single map? Does it allow to assign and verify remediations in your work tools? Does it measure impact in terms of deleted attack paths, not just applied patches? Questions like these separate solutions that generate "a lot of noise" reports from those that provide measurable risk reduction.
The arrival of the Exposure Assessment Platforms concept and its inclusion in Gartner's Magic Quadrant makes it clear that the market is evolving towards more contextual and operational models. For teams with limited budgets and time, this is not a luxury: it is the difference between working a lot and achieving little, or working more directed and producing results that matter to business. If you want to look into how some suppliers have positioned themselves on this new map, you can see Gartner's report cited above and a press release from a market actor who shares his assessment Here..
In the end, the invitation is simple: it reposes the question that guided the management of vulnerabilities for years. Instead of counting how many failures you detect, ask if your organization is protected from the path of attack that really matters. This change of approach is, today, the best way for security to stop being a noisy cost centre and become a measurable resilience factor.

Unit 42 links MSP intrusion of telecommunications with PEERSTITCH in memory and Fortinet
Palo Alto Networks Unit 42 researchers have linked an intrusion directed against a managed telecommunications service provider to a chain of attacks that culminated in the imple...
Linux Kernel allows host memory reading from a VM; CVE-2026-99999 patch.
The security community has confirmed a critical vulnerability in the Linux kernel network code that allows code that is already running within a virtual machine (VM) to read mem...
Laboratory shows code execution in Windows SFAPE enclave (CVE-2026-83498) and patch
Researchers at the Doyensec firm have shown in laboratory that it is possible to run code chosen by an attacker within a portion of Windows memory that should remain sealed even...
Safety report of agents IA: 1,280 products, 282 with SSO; majority without identity control
A new report on the safety of IA agents presents a worrying but concrete picture: in the environments examined for the 2026 State of Agent Security Report There are about 1,280 ...
Campaign with LLM and ARTEX attacks South Korean financial institutions and exfilters data
Security researchers have documented a campaign directed against South Korean financial institutions using language-driven attack tools to automate intrusions and data extractio...
Cybersecurity report: defense is no longer a point, it is continuous visibility and scalable response
A new public report on cybersecurity describes how cloud expansion, artificial intelligence and distributed systems are changing the goal and protection priorities: it is no lon...