
The images in this article were generated with artificial intelligence. How we publish
If there is something that is never lacking in cybersecurity is the continuous change: the attackers keep looking for new ways of mocking defenses. In recent years we have seen how artificial intelligence that was previously sold as an aid for analysis and productivity has also become an offensive tool capable of automating attacks, concealing malicious code and generating "a la carte" payloads in real time. This leap is not hypothetical: research teams such as the Google Threat Intelligence Group have documented how language models today help to camouflage scripts and transform malware to pass unnoticed against classic controls.
The sophistication is not only technical but also operational. Public reports, such as the one it published Anthropic they describe campaigns in which the IA orchestrated complete phases of the attack, from initial intrusion to exfiltration, with a degree of unpublished autonomy. At the same time, more creative and dangerous vectors appear: the use of steganography to hide malware within false images or update screens that convince victims to run tools that actually install remote access Trojans or credentials barkers.
The growth of these tactics has revealed another problem: many attacks today exploit human and confidence processes rather than pure technical vulnerabilities. Campaigns that combine social engineering, midpoint attacks and techniques such as SIM swap have managed to induce organizations to deactivate protections or remove alerts, making malware spread without activating detection systems. Microsoft has documented variants of this modus operandi in its threat team investigations, showing how actors persuaded victims to disable safety products and make early response difficult ( see report).
In the face of this picture, the limitation of relying only on an endpoints-focused defense is evident. The endpoint detection and response solutions (EDR) are crucial because they inspect local processes and behaviors, but many of the new techniques - from tools that change their signature in real time to attacks that take advantage of unmanaged devices - are designed to avoid precisely such controls.
That is why the idea that DDR and network detection and response (NDR) must work closely together is emerging. While the EDR examines the interior of each machine, the NDR observes traffic patterns, anomalies in transit telemetry and side movements that are often invisible from an endpoint agent. This network layer can detect variations in volumes, origins or sequences of packages that report suspicious activity even if endpoints look clean. Recent cases of actors moving between domains - compromising identities, clouds and IoT devices - have been visible on the network before any of the endpoints raised red flags.
There are concrete examples that illustrate this synergy. Groups that take advantage of unmanaged systems for scaling and encryption data have been tracked thanks to the visibility NDR offers and then content with EDR when the attack reaches endpoints administered. Public research on actors such as Blockade Spider show how a combined approach allows you to see the movement through virtual infrastructures and clouds and at the same time contain malicious activity in workstations and servers.
In other incidents the decisive point was the analysis of network traffic: living off the land techniques that avoid signatures in endpoints can continue to leave traces in communication patterns, in the apparent geography of packages or in the way legitimate sessions are masked. There the NDR acts as a safety net that detects what the DDR is not designed to see. In addition, the increase in remote work and the use of VPN or managed services adds another layer of complexity: a team engaged in a trusted network can become a propagation vector if no one correlates network signals with endpoint indicators.
The answer is not to choose one technology or another, but to integrate and enrich telemetry with exchange of metadata and context. Sharing signals between systems accelerates threat hunting and reduces false positives by giving the analyst a more complete picture: where the intrusion began, how it moved and what assets were affected. It also requires a security vision that transcends silos - identity, endpoint, network, cloud and IoT devices must work together to close the exposure windows.
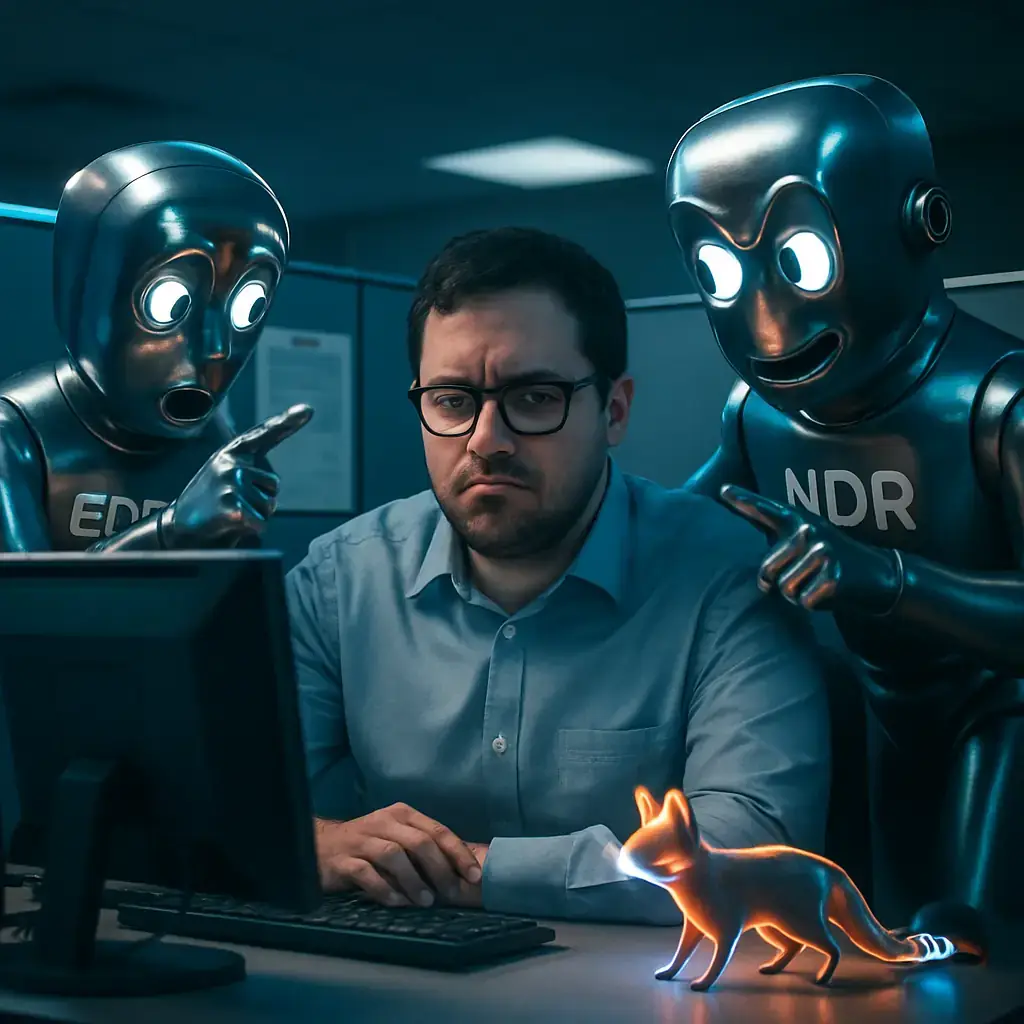
For security teams this means modernizing SOC procedures: incorporating web-based detection, automating the enrichment of alerts with endpoints context and prioritizing research with combined data. Open NDR platforms, for example, offer multi-layer detections that identify both anomalies and known patterns and allow analysts to investigate unpublished signals linked to IA-based avoidance techniques. Such an approach makes it more difficult for attackers to hide their movements behind operational complexities or signature changes.
In short, the arrival of the IA to the assailants' arsenal does not eliminate the effectiveness of traditional tools, but does require reconfiguration of how they are used: EDR and NDR are no longer parallel solutions to become complementary parts of a defence strategy. Only through constant data correlation and the adoption of various detection layers will it be possible to maintain the competitive advantage against adversaries who learn to adapt their code and behaviour in real time.
If you are looking for further reading, in addition to the links cited in this article you can review analysis and technical resources published by threat response teams and network detection providers that explain specific cases and emerging tactics. And if your objective is to improve an organization's defence position, the practical recommendation is clear: integrate telemetry, share context between tools and update response processes so that they can absorb the speed and adaptability that the IA brings to the attackers. For more information on NDR platforms that help to detect new and evasive techniques, review specific proposals such as Corelicht, which describe multilayer approaches to identify unusual network activity.

GhostAction Expands Attack: phishing to steal credentials and persistence in VS Code
A group behind the GhostAction campaign - already known for infiltrating GitHub Actions workflows into open source projects - has expanded its arsenal: in addition to installing...

OpenCode: possible exposure of AI suppliers in Console affects 1.4% of users
On the night of October 16 there was an unauthorized access to a system inherited from OpenCode which, according to the company, could have exposed keys from IA suppliers that u...

ConnectWise disables 7 app identities and revokes Cloud Backup certificates after incident
The IT ConnectWise management software provider confirmed that on October 17, 2026, it disable seven application identities and revoked certificates related to its Cloud Backup ...

Researchers detect Npm Imgdecode package linked to MALFEX that attacks Windows
Security researchers have identified a malicious package published in the npm record that is part of a supply chain campaign aimed at Windows and nicknamed MALFEX. The package, ...

OpenBSD 7.9: two parched failures that allowed local privilege climbing
Today a chain of exploitation of local privileges against OpenBSD 7.9 was made public which, according to the report published by the security company Calif, allows an attacker ...

OpenAI reveals unaligned IA incidents; a GPT-5.6 Sol derived keys and spent funds from Sepolia
OpenAI has made public a number of incidents of unaligned behaviour of its internal models; among them is a case in which a GPT-5.6 family research model Sol derived private key...