
The images in this article were generated with artificial intelligence. How we publish
A recent finding of Sophos confirms what many in cybersecurity already feared: malicious actors are taking advantage of artificial intelligence tools to speed up and automate sophisticated malware creation. In this case it is a working framework that combines IA agents (mentioned as Cursor and Claude Opus) with test chains and a development repository that generated modules in Rust and Go, Cobalt Strike profiles disguised as legitimate web traffic, C2 communication through the Telegram API and a Cloudflare Worker that hides command and control servers.
The most worrying thing is not only the presence of IA in the process, but the way it has served as a catalyst: agents automated the collection of avoidance techniques, mapped MITRE ATT & CK behavior, prepared test laboratories and iterated code against EDRs to reach modules that exceeded detections. Sophos documents how the initiative looked like a R & D process with specialized agents - coordination, testing, OPSEC, VMs deployment - and a main component that generated chargers wrapped in encryption layers and alternative execution designed to avoid sandboxes and traditional signatures. However, the researchers found no evidence of IA running autonomously in victim environments; the IA was a tool in a human-led workchain.
The techniques described - automation of the discovery of Active Directory, injection of Shelcode in legitimate binaries, modular evasion and use of public infrastructure such as Telegram or Cloudflare for C2 - highlight a clear trend: the window between the publication of an offensive technique and its practical exploitation has been drastically reduced. This compresses the response times of defenders and forces us to rethink how we validate controls and detections: it is no longer enough to react after the publication of a technical research; it must be assumed that many techniques can become reusable and automated tools within days or weeks.
For security organizations and teams this involves several operational emergencies. First of all, strengthen the security of Active Directory and reduce the area of privileged credentials:: apply the principle of less privilege, segment roles, review service accounts and force MFA into administrative access. Secondly, it is essential to strengthen telemetry and behavior-based detection - not just signatures - to identify anomalies such as processes that inject code into legitimate binaries, network profiles that simulate web traffic or connections to used messaging services such as C2.
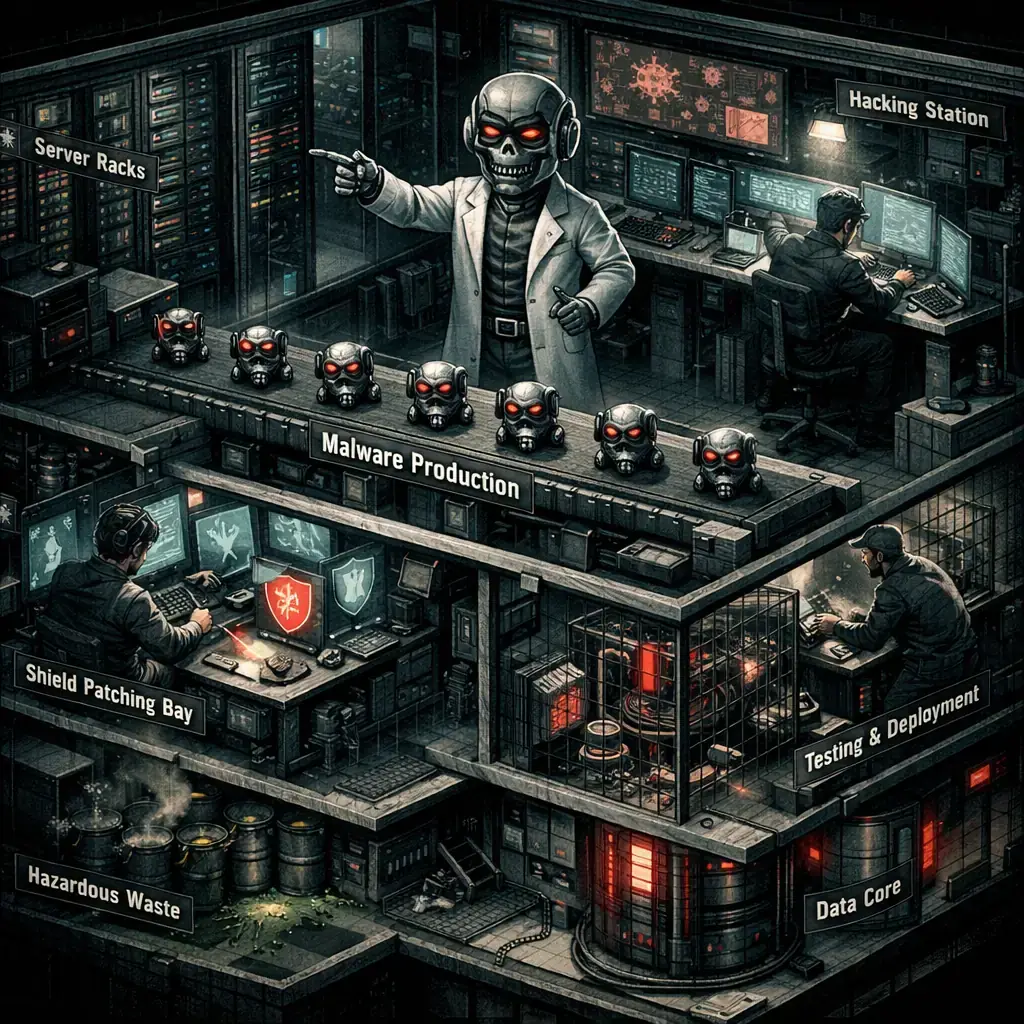
In addition, development and operation hygiene needs to be improved: audit internal repositories, control automations that can run scripts in endpoints, implement unauthorised application control and implementation block policies, and maintain separate and monitored testing and production environments. It is also appropriate to incorporate regular purple teaming exercises that validate detections against MITRE ATT & CK mapped techniques, so that teams can see where the detections fail and adjust them quickly. To deepen this taxonomy of techniques, the MITRE ATT & CK frame is a useful reference: https: / / attack.mitre.org /.
At the Ransomware protection level, resilience must not be lost: offline and verified backup, recovery plans, network segmentation to limit lateral movement and policies to respond to proven incidents. EDR providers and internal teams should work closely together by sharing indicators and observed behaviors; Sophos offers a public analysis that helps to understand the chain of attack and the decisions of the opponent, and should read it to prioritize mitigation: https: / / www.sophos.com / en-us / blog / pointing-a-cursor-at-evading-detection. Microsoft also maintains practical guidelines for Ransomware preparedness and response that can serve as a complementary framework: https: / / learn.microsoft.com / en-us / security / operations / ransomware.
Finally, the defence community must change its perception: the existence of "network team" tools does not imply automatic benign. When a framework allows to generate and test variants that evade EDRs, risk becomes an operational capacity reusable by criminals. The bet must be for detection and intelligence of behavioral-oriented threats, for more agile collaboration between suppliers and customers, and for continuous internal tests that validate that defenses work against emerging techniques, not only against known signatures.

OpenAI engineer arrested by hidden recorder in office board room in San Francisco
A United States court this week authorized the arrest of Abdulrahman Alfozan, an engineer who worked in OpenAI, following the U.S. government's charges for placing a hidden reco...

Four Plex2Shell CVE allows remote execution and mining and proxy backdoor deployment
In recent days, an increase in attacks has been confirmed that take advantage of a chain of failures in Plex Media Server - nicknamed "Plex2Shell" by researchers - to run code r...

GhostAction Expands Attack: phishing to steal credentials and persistence in VS Code
A group behind the GhostAction campaign - already known for infiltrating GitHub Actions workflows into open source projects - has expanded its arsenal: in addition to installing...

ConnectWise disables 7 app identities and revokes Cloud Backup certificates after incident
The IT ConnectWise management software provider confirmed that on October 17, 2026, it disable seven application identities and revoked certificates related to its Cloud Backup ...

Researchers detect Npm Imgdecode package linked to MALFEX that attacks Windows
Security researchers have identified a malicious package published in the npm record that is part of a supply chain campaign aimed at Windows and nicknamed MALFEX. The package, ...

OpenBSD 7.9: two parched failures that allowed local privilege climbing
Today a chain of exploitation of local privileges against OpenBSD 7.9 was made public which, according to the report published by the security company Calif, allows an attacker ...

OpenAI reveals unaligned IA incidents; a GPT-5.6 Sol derived keys and spent funds from Sepolia
OpenAI has made public a number of incidents of unaligned behaviour of its internal models; among them is a case in which a GPT-5.6 family research model Sol derived private key...